A security analyst checks for risks to a company’s systems and information, investigates suspicious activity and helps improve security.
The title can describe monitoring, vulnerability reviews or work with security policies. Information security analyst is also a broader occupation tracked by the U.S. Bureau of Labor Statistics.
Ad
cybersecurityguide.org is an advertising-supported site. Clicking in this box will show you programs related to your search from schools that compensate us. This compensation does not influence our school rankings, resource guides, or other information published on this site.
Featured Information Security Training
| School Name | Program | More Info |
|---|---|---|
| Southern New Hampshire University | Online BS in Computer Science - Information Security | website |
| UC Berkeley School of Information | Online MS in Cybersecurity | No GRE/GMAT Required | website |
| Arizona State University | Online BS in Information Technology - Cybersecurity | website |
What Does a Security Analyst Do?
Analysts review security alerts and records, investigate suspicious logins or malware warnings, identify weaknesses, and explain which actions are needed. They document their findings so other teams can respond or make improvements.
An alert alone does not prove an attack. For example, an unfamiliar login location might reflect a VPN or business travel. The analyst checks sign-in and device records before deciding whether the case needs escalation.
Security Analyst vs. SOC Analyst vs. GRC Analyst
| Job title | Main emphasis |
|---|---|
| Security analyst | General security monitoring, reviewing weaknesses or improving safeguards |
| SOC analyst | Investigating alerts and handing off or responding to incidents |
| GRC analyst | Reviewing security policies, controls, risk and audit evidence |
SOC means security operations center; GRC means governance, risk and compliance. Duties overlap, so check individual job descriptions.
Tools and Skills That Matter
The job often involves searching logs, which are records of events such as account sign-ins or device activity. A SIEM combines records to help analysts investigate; EDR tools help examine potentially harmful activity on devices.
- Log and alert investigation: Microsoft Sentinel and similar SIEM platforms help build an incident timeline.
- Device investigation: Microsoft Defender for Endpoint and similar tools show endpoint warnings and activity.
- Vulnerability work: Analysts may use scanners and prioritization information to recommend fixes.
- Clear reporting: Every team needs analysts who can explain what the evidence shows and what remains uncertain.
Some positions use scripts or query languages; advanced coding is not a universal requirement.
How to Get Started
Choose the kind of analyst vacancy that interests you, then look for ways to demonstrate that work. A sample project might involve investigating an invented suspicious login alert, building a timeline, considering alternative explanations, and writing a brief report.
A vulnerability-focused applicant can show how they prioritized and verified fixes in an authorized practice system. Never test systems without permission.
IT support, systems administration, cloud support, internships, and junior security operations can provide relevant experience. The BLS lists a computing-related bachelor’s degree and relevant work experience as typical for the broader occupation, while individual jobs may differ.
For certifications, ISC2 CC requires no previous work experience, Security+ covers broad security knowledge, CySA+ focuses more on analysis, and GIAC GCIH addresses incident handling. Advanced CISSP certification has qualifying experience rules.
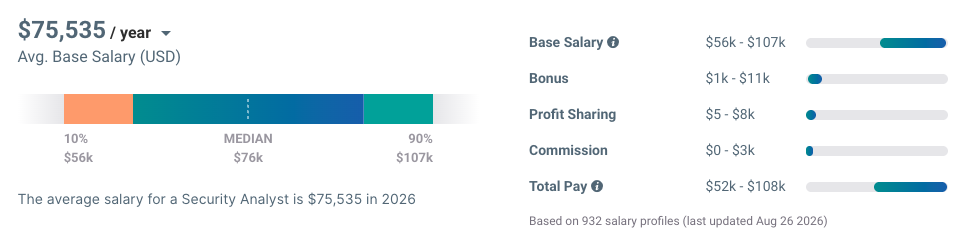
Salary and Job Outlook
| Source | U.S. annual pay | Measure |
|---|---|---|
| BLS | $129,180 | Median for broad Information Security Analysts occupation |
| Indeed | $101,565 | Average base salary from roughly 1,300 posting-derived observations |
These are different groups and methods, not competing versions of one exact-title salary. Neither represents guaranteed starting pay.
BLS forecasts 21% employment growth for information security analysts from 2025 to 2035 and about 14,100 openings per year on average. This is not an SOC-analyst-only projection.
Frequently Asked Questions
Sometimes. SOC work centers on monitoring and investigating incidents; broader analyst roles can also cover vulnerability and control reviews.
Not for every job. Some employers accept relevant IT work, technical training or internships, while a related bachelor’s degree and experience are typical for the broader BLS occupation.
Some junior roles suit applicants with practical training and related experience. Other positions require prior IT or security work.
Not always. Reading log queries and simple scripts is often more useful than advanced software development for monitoring roles.
Start with the tools used in your target vacancies. For SOC work, practice examining sample logs and endpoint events; for vulnerability work, practice evaluating permitted findings.
Yes. Work with incidents, security controls and technical fixes can support a move into security engineering. See the Security Engineer guide.
References
- BLS | Information Security Analysts Outlook | Accessed October 2026
- O*NET | Information Security Analysts | Accessed October 2026
- Microsoft | Microsoft Sentinel incident investigation in the Azure portal | Accessed October 2026
- ISC2 CC | CC – Certified in Cybersecurity | Accessed October 2026
- Indeed | Salary information | Accessed October 2026