A business information security officer (BISO) helps a business unit make informed cybersecurity decisions.
The BISO connects department leaders with the central security team, explains business risks, and follows up on security problems that affect operations. It is typically an experienced advisory or leadership role.
Ad
cybersecurityguide.org is an advertising-supported site. Clicking in this box will show you programs related to your search from schools that compensate us. This compensation does not influence our school rankings, resource guides, or other information published on this site.
Featured Cybersecurity Training
| School Name | Program | More Info |
|---|---|---|
| Purdue Global | Online BS in Cybersecurity | website |
| UC Berkeley School of Information | Online Master’s in Cybersecurity | No GRE/GMAT Required | website |
| Arizona State University | Online BS in Information Technology - Cybersecurity | website |
| Southern New Hampshire University | Online BS in Cybersecurity or Online MS in Cybersecurity | website |
What does a BISO do?
A BISO may review new business projects, cloud services, suppliers, and security exceptions. They help leaders understand what could go wrong, which controls need improvement, and who should make the final decision.
The FS-ISAC BISO role guide describes different reporting structures, including ties to both a business unit and the chief information security officer (CISO).
An illustrative example: a department plans to launch a service while a serious security issue remains unresolved. The BISO explains the potential business impact, works with the technology team on options, identifies who owns the fix, and records the decision for the authorized leader.
A BISO does not automatically approve every risk or lead every technical incident investigation.
BISO, CISO, and GRC roles: the difference
| Role | Usual focus |
|---|---|
| BISO | Cyber risk and security decisions for an assigned business area |
| CISO | Organization-wide security leadership and governance |
| GRC analyst | Control testing, audit evidence, policy reviews, and risk records |
The BISO title can also appear as business security lead or a similar position. Employers define responsibilities differently. See the CISO career guide for the executive role.
How to prepare for BISO work
Most BISO openings seek experience dealing with both cybersecurity and business decisions. A 2026 Bank of America BISO posting requests two to five years of technology experience and at least five years in information security for that particular position.
It also emphasizes risk assessments, tracking fixes, reviewing exceptions, and explaining findings to business leaders.
Useful experience includes leading control reviews, assessing vendor risks, presenting options to management, and coordinating remediation across teams.
Degrees in cybersecurity, computing, risk, and business can support this work. CISM, CRISC, and CISSP are relevant to different parts of the job.
Full certification requires qualifying experience: five years for CISM, three for CRISC, and normally five for CISSP, with a possible one-year CISSP reduction.
BISO salary in the United States
| Source | U.S. annual figure | Measure |
|---|---|---|
| Indeed | $151,488 | Average base salary; 53 posting-derived observations |
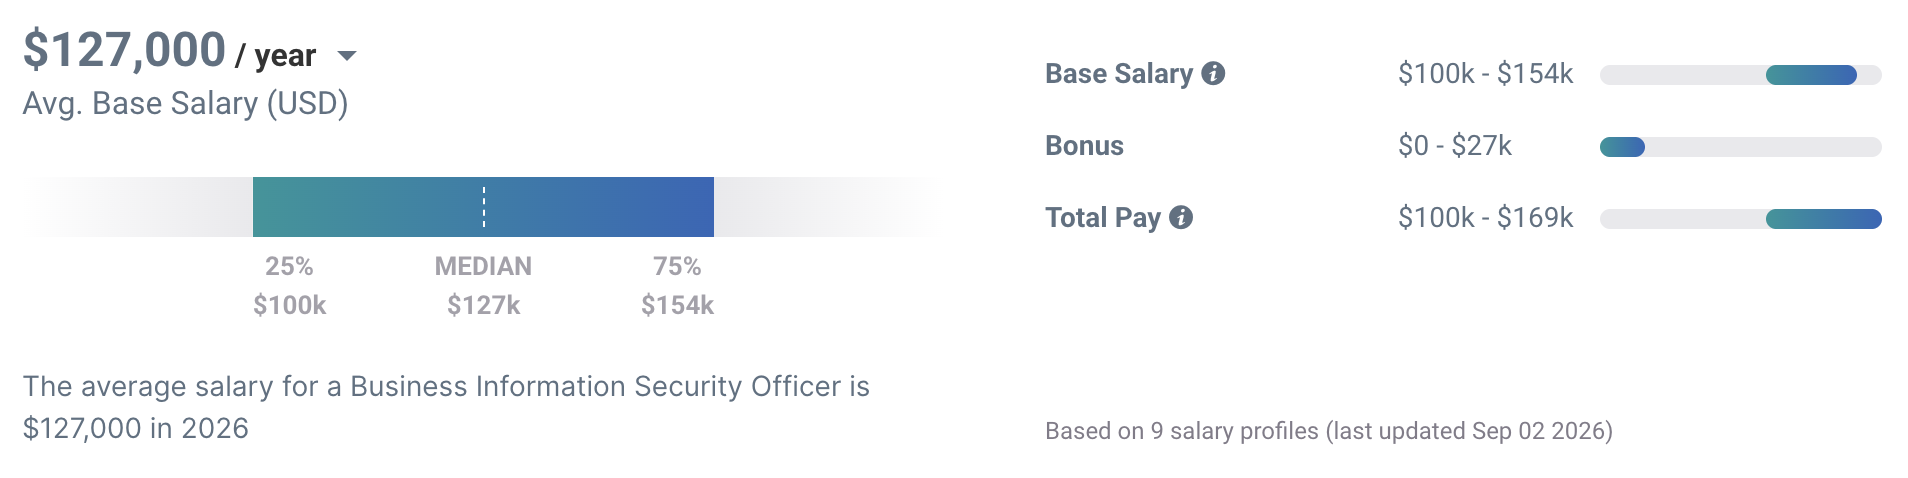
| PayScale | $127,000 | Average base salary; only nine profiles |
| Salary.com | $79,781 | Published average annual salary estimate |
For local context, Bank of America’s 2026 posting lists $99,200–$145,000 in annual salary for its BISO role in Colorado and Illinois. That is a specific advertised range, not a national benchmark.
BISO job outlook
The Bureau of Labor Statistics does not track BISOs as an exact-title occupation. Its broader computer and information systems managers group has a May 2025 median wage of $175,140 and projected 16% growth from 2025 to 2035. Neither statistic is specifically for BISOs.
Frequently asked questions
No. A CISO generally directs enterprise security, while a BISO focuses on the security needs of assigned business units.
Explaining security risks in business terms and helping the right people make and carry out decisions. Technical knowledge supports that judgment.
No. Some BISOs manage teams, but many coordinate work across teams without directly supervising the engineers.
Yes. Risk reviews, audit findings, exception management, and management reporting are relevant experience, especially when combined with solid cybersecurity understanding.
The authorized business leader or governance body makes the decision under company policy. A BISO helps explain, document, and escalate the risk.
References
- FS-ISAC | BISO role guide | Accessed November 2026
- NIST | CSF 2.0 | Accessed November 2026
- Bank of America | Job posting | Accessed November 2026
- ISACA | CISM Certification | Accessed November 2026
- ISACA | CRISC Certification | Accessed November 2026
- ISC2 | CISSP Certification | Accessed November 2026
- Indeed | BISO salary information | Accessed November 2026
- PayScale | BISO salary information | Accessed November 2026
- Salary.com | BISO salary information | Accessed November 2026